

External Network & Perimeter Assessments: CA$5,000–CA$15,000
Assesses public-facing IP addresses, firewalls, open ports, exposed services, and external security misconfigurations.
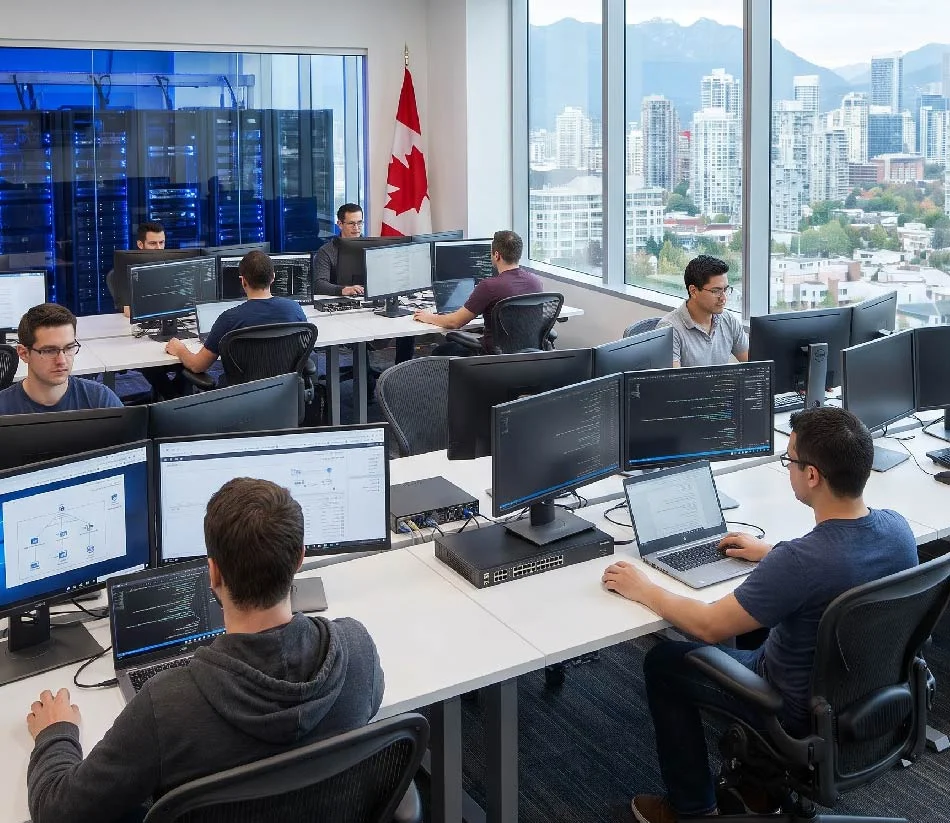
Maintaining a strong posture in Canada’s digital ecosystem requires proactive defense against increasingly sophisticated ransomware attacks, supply-chain vulnerabilities, and rigorous regulatory demands. Securing digital infrastructure demands targeted penetration testing services in Canada aligned with local compliance frameworks like PIPEDA and regional data privacy standards.
Partnering with a specialized provider ensures your web applications, mobile platforms, cloud environments, and internal networks are thoroughly evaluated by top security analysts. Modern security testing combines rigorous manual exploitation with continuous risk analysis to expose technical flaws before malicious threat actors can exploit them.
StrongBox IT is a global cybersecurity leader offering specialized penetration testing services for Canadian enterprises. Known for its developer-centric approach and thorough manual testing methodologies, StrongBox IT, delivers deep technical evaluations across web applications, APIs, cloud environments, and internal networks. Our actionable reporting and seamless retesting frameworks make us a top choice for organizations seeking robust compliance alignment and zero-false-positive assurances.
Based in Toronto, Packetlabs is a specialized cybersecurity firm focused exclusively on offensive security assessments. Certified in CREST and SOC 2 Type II, Packetlabs goes beyond simple automated scanners to deliver deep manual penetration testing, red teaming, and ransomware readiness assessments for Canadian mid-market and enterprise clients.
eSentire is a global authority in Managed Detection and Response (MDR) and offensive security services. They offer strategic penetration testing, threat hunting, and web application assessments designed to help heavily regulated industries—such as healthcare and finance—defend their infrastructure.
Software Secured specializes in application security and continuous penetration testing (Penetration Testing as a Service - PTaaS). They work closely with SaaS companies and software development teams across Canada to integrate security directly into agile CI/CD pipelines.
Forward Security provides information security and penetration testing services tailored to the finance, tech, and healthcare sectors. Their team focuses on cloud security, application security assessments, and enterprise architecture protection.
Founded in Toronto, Cyderes is an enterprise cybersecurity provider offering managed security services, SOC operations, and full-scope penetration testing. They assist large Canadian organizations in aligning with complex governance, risk, and compliance mandates.
Security Compass is a major player in software security. Alongside their advisory and training platforms, they deliver targeted threat modeling and application penetration testing services to ensure secure software lifecycles.
Qualysec is a recognized cybersecurity firm providing comprehensive VAPT services to Canadian businesses. Utilizing a combination of automated tooling and expert manual analysis, they offer specialized pentesting for web apps, mobile solutions, APIs, and cloud architecture.
Deloitte’s Canadian risk advisory practice provides enterprise-grade cybersecurity solutions. Their dedicated penetration testing teams conduct large-scale network infrastructure audits, regulatory readiness assessments, and complex adversary simulations for enterprise and public-sector organizations.
Vumetric is a specialized Canadian firm dedicated to information security assessments and penetration testing. It provides a tailored network, ISO 27001, and PCI-DSS compliance-driven penetration tests for businesses across Canada.
Ensure the firm’s technical team holds industry-recognized, hands-on certifications rather than basic multiple-choice credentials:
OSCP (Offensive Security Certified Professional)
The industry standard for practical, hands-on penetration testing skills.
OSCE³ (Offensive Security Experienced Expert)
An advanced credential demonstrating expertise in exploit development, advanced web attacks, and enterprise network evasion.
CREST
Gold-standard organizational and individual accreditation ensuring strict ethical, legal, and technical quality.
GPEN (GIAC Penetration Tester)
Demonstrates comprehensive mastery of formal pentesting methodologies and conduct.
Your chosen firm must understand how to map vulnerability findings directly to compliance frameworks governing Canadian operations:
Your chosen firm must understand how to map vulnerability findings directly to compliance frameworks governing Canadian operations:

PCI-DSS
Mandates annual internal/external penetration tests and segmentation validation for payment processing.
SOC 2 Type II
Requires technical proof that security controls effectively prevent unauthorized system access.
OSFI Guidelines (for Financial Institutions)
Requires rigorous cyber resilience testing and third-party risk management.

Actionable Reports
A high-quality report must include an executive summary for business leadership, along with detailed technical write-ups, validation details, and specific remediation guidance for developers.
Retesting Policy
Vulnerability fixes can fail or introduce new issues. Ensure your vendor provides free or clear-cost retesting within 30 to 60 days to verify that all reported flaws are fully remediated.
Under Canadian privacy legislation, sending sensitive network diagrams, data samples, or vulnerability reports across international borders can trigger compliance violations. Ensure your vendor adheres to PIPEDA (Personal Information Protection and Electronic Documents Act), uses Canadian data residency options for report storage, and executes strict Non-Disclosure Agreements (NDAs).
For most small-to-midmarket organizations in Canada, a professional penetration test typically costs between CA$5,000 and CA$45,000+, while large-scale enterprise assessments and red team exercises can exceed CA$150,000.
The final cost depends on the size of the environment, testing scope, technical complexity, number of assets, and specific compliance requirements.

Assesses public-facing IP addresses, firewalls, open ports, exposed services, and external security misconfigurations.
Costs vary based on application complexity, business logic, API endpoints, input fields, authentication mechanisms, and user privilege levels.
Covers internal networks, workstations, Active Directory environments, privilege escalation, and potential lateral movement paths.
Evaluates IAM policies, cloud configurations, storage permissions, containers, serverless functions, and other cloud security controls.
Simulates realistic attacks using multiple techniques, which may include physical security testing, social engineering, and advanced attack scenarios.
Provides continuous or recurring security testing throughout the year, helping organizations identify and validate vulnerabilities beyond a single assessment.
When safeguarding digital assets, settling for basic automated scans leaves businesses vulnerable to modern threat vectors. StrongBox IT delivers enterprise-grade penetration testing services in Canada designed to identify critical security gaps before attackers do.
Our certified ethical hackers combine hands-on manual testing with deep technical expertise to ensure your web applications, APIs, cloud environments, and networks remain secure and compliant with PIPEDA and global standards. Partner with a premier penetration testing company in Canada that prioritizes zero false positives, clear remediation roadmaps, and dedicated retesting support.
A penetration test in Canada typically costs CA$5,000 to CA$45,000+, depending on the scope, number of assets, testing complexity, and compliance requirements.
A vulnerability scan uses automated tools to identify known weaknesses, while a penetration test combines automated scanning with manual testing to safely validate and exploit security vulnerabilities.
PIPEDA does not explicitly mandate penetration testing, but organizations must use appropriate safeguards to protect personal information. Penetration testing can help demonstrate and validate the effectiveness of security measures.
Companies should generally conduct penetration testing at least annually and after major infrastructure, application, or network changes, with higher-risk environments requiring more frequent assessments.
A penetration test typically takes several days to a few weeks, depending on the scope, number of systems, testing methods, and complexity of the environment.
