


The Payment Card Industry Data Security Standard mandates annual internal and external penetration testing—as well as after any major infrastructure change—for entities handling credit card transactions.
Best VAPT Services in Hyderabad
Protect your IT ecosystem, cloud infrastructure, and enterprise applications with premier VAPT services in Hyderabad. As the cyber threat environment continues to evolve, organizations operating across Hyderabad’s leading technology corridors face increasingly sophisticated and targeted cyber threats.
Comprehensive VAPT testing combines automated scans with manual, hands-on penetration testing to safeguard critical assets before attackers can exploit them.
What Is VAPT?
Vulnerability Assessment and Penetration Testing (VAPT) is a comprehensive cybersecurity evaluation process designed to detect, analyze, and mitigate security weaknesses across your IT infrastructure:
- Vulnerability Assessment: An automated and systematic identification of known security flaws, configuration issues, and patch gaps across networks, systems, and applications.
- Penetration Testing: A human-led, simulated cyberattack that safely attempts to exploit detected vulnerabilities, proving their real-world impact and depth of risk.
Together, VAPT services give organizations a clear, actionable picture of their security posture.
What Is VAPT?
Why Does a Business Need VAPT Services in Hyderabad?
As Hyderabad continues its rise as a premier global hub for IT, Fintech, Healthcare, and SaaS innovation, local enterprises are prime targets for cyberattacks.
Partnering with a trusted provider of VAPT services in Hyderabad ensures:
VAPT Service

Proactive Threat Mitigation
Identify hidden zero-day risks and system misconfigurations before cybercriminals find them.

Data Loss Prevention
Safeguard sensitive customer records, proprietary software source code, and financial transactions.

Regulatory & Compliance Assurance
Meet stringent Indian and international cybersecurity standards.

Brand Reputation & Trust
Maintain customer and stakeholder confidence by maintaining a resilient cybersecurity defense.
Types of VAPT Services We Offer for Hyderabad Companies
To provide end-to-end security, our VAPT offerings cover every critical vector of your digital ecosystem:
Network VAPT
We evaluate both internal and external network architectures. Our certified security engineers audit routers, firewalls, switches, and active directory structures to eliminate unauthorized entry points and lateral movement risks.
Web Application VAPT
Web applications are often the primary entry point for cyberattacks. Our application-level vulnerability assessment and penetration testing cover OWASP Top 10 risks, including SQL Injection (SQLi), Cross-Site Scripting (XSS), Broken Authentication, and Business Logic Flaws.
API Security Testing
APIs connect your internal systems and data, making them prime targets for cyberattacks. We thoroughly test your REST, SOAP, and GraphQL APIs to uncover unauthorized access risks, data leaks, and code injection vulnerabilities.
Mobile Application VAPT
Whether Android or iOS, mobile applications require deep security checks. We analyze binary security, reverse-engineering risks, local data storage leaks, and insecure network communications following OWASP MASVS standards.
Cloud Security Testing
Migrating to AWS, Azure, or Google Cloud requires continuous cloud security oversight. Our cloud VAPT services review IAM roles, bucket permissions, serverless architecture risks, and container configurations.
IoT Security Testing
Connecting smart hardware to enterprise networks introduces unique entry points. We inspect IoT device firmware, communication protocols, hardware interfaces, and backend cloud connections.
Internal & External VAPT
- External VAPT: Simulates an external threat actor targeting your internet-facing assets (websites, firewalls, public IP blocks).
- Internal VAPT: Simulates an insider threat or an attacker who has already breached the perimeter, evaluating internal access controls and lateral movement potential.
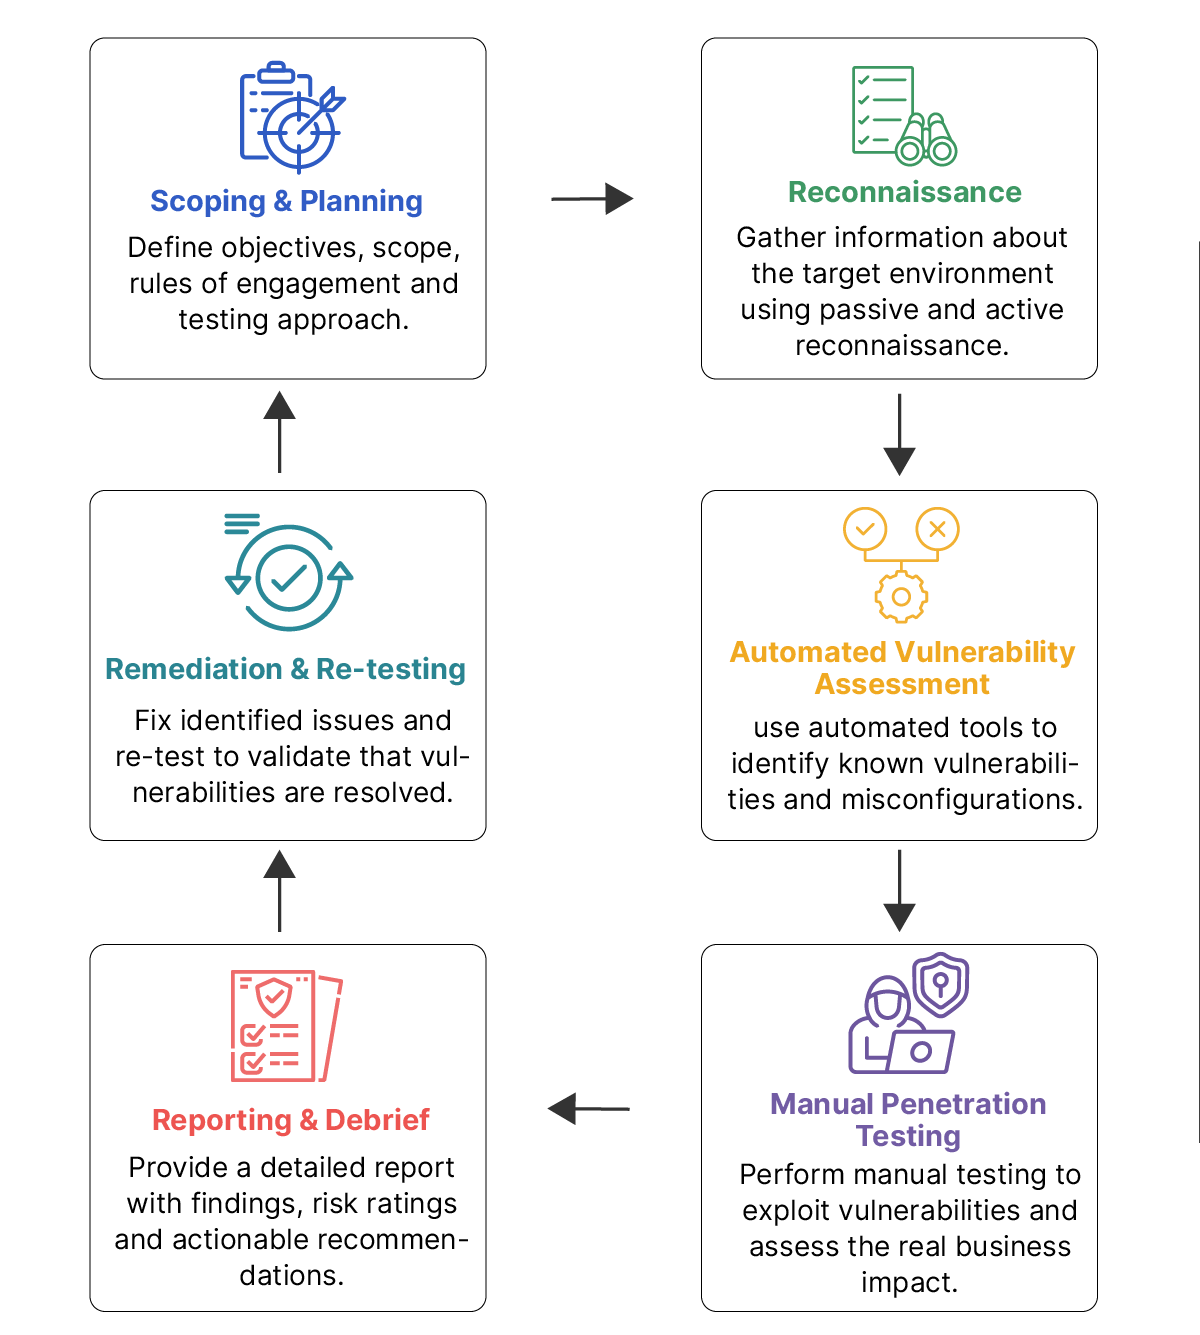
Our Approach to Vulnerability Assessment & Penetration Testing
We follow a structured, globally recognized security framework aligned with leading industry standards:
Who Needs VAPT Services?
Any organization that stores, processes, or transmits sensitive data requires regular VAPT assessments. Key sectors in Hyderabad including:

SaaS & Technology Startups
Protecting digital platforms and IP prior to product launches or investor audits.
Fintech & Banking Entities
Securing financial transactions, payment gateways, and customer accounts.
Healthcare & Healthtech Providers
Safeguarding sensitive patient health records (PHI/EHR).
E-Commerce & Retail Outlets
Protecting payment flows, user accounts, and customer databases.
Government & Enterprise Agencies
Meeting critical infrastructure security benchmarks.
Certifications & Compliance Standards That Require VAPT
Executing periodic VAPT security testing is a non-negotiable requirement for major compliance frameworks:

PCI DSS Penetration Testing

ISO 27001
Clause 8.8 (Management of Technical Vulnerabilities) requires organizations to conduct regular vulnerability assessment engagements to maintain Information Security Management Systems (ISMS) compliance.

SOC 2
To achieve SOC 2 Type II attestation, organizations must demonstrate proactive risk management through ongoing VAPT services and threat monitoring.

HIPAA
Healthcare organizations must verify administrative and technical safeguards through security evaluation services to prevent protected health information leaks.

GDPR
Articles 32 & 35 mandate regular testing, assessing, and evaluating of technical measures to maintain data processing security.
RBI & Industry-Specific Requirements
The Reserve Bank of India (RBI), IRDAI, and SEBI enforce strict periodic VAPT audits for all regulated financial institutions, fintech firms, and payment gateways.
How Often Should VAPT Testing Be Conducted?
Cyber risks change every time your systems update. To maintain strong defense posture, VAPT testing should be conducted:

Annually or Semi-Annually
As part of standard risk governance and regulatory compliance schedules.

After Major Updates
Following major code releases, cloud migrations, or network redesigns.

Prior to Product Launches
Ensuring new web or mobile applications are secure before public deployment.

Post-Incident
Assessing infrastructure following a breach or near-miss to close verified vectors.
Benefits of Conducting VAPT Testing
Investing in professional VAPT services in Hyderabad delivers tangible operational advantages:
- Prevent Financial Losses: Avoid costs associated with data recovery, legal fines, and ransom demands.
- Speed Up Sales Cycles: Provide security attestation letters to enterprise prospects during vendor procurement security reviews.
- Minimize Downtime: Keep web applications, databases, and network services operational by avoiding disruptive exploits.
- Prioritize IT Security Spend: Direct budget directly toward remediating high-risk vulnerabilities.
Why Choose StrongBox IT for VAPT Services in Hyderabad?
StrongBox IT combines deep technical expertise with tailored execution strategies to protect organizations against sophisticated cyber threats.
- Certified Ethical Hackers: Our engineering team holds recognized certifications (CEH, OSCP, CISSP).
- Zero False-Positives Guarantee: Every automated vulnerability result is manually verified before reporting.
- Comprehensive Remediation Support: We work alongside your development team to guide patching efforts.
- Complimentary Re-Testing: We re-assess your systems post-patching to confirm vulnerabilities are fully resolved.
Strengthen Your Security with VAPT Services in Hyderabad
Strengthen Your Security with VAPT Services in Hyderabad
Don't wait for a data breach to expose hidden vulnerabilities in your IT infrastructure. Contact our team today to schedule your VAPT assessment and receive a customized security roadmap for your business.

FAQ
A vulnerability assessment is an automated scan that identifies known security flaws across systems. A penetration test is a manual, simulated cyberattack in which certified security testers actively attempt to exploit those flaws to determine their real-world impact.
Yes. PCI DSS explicitly mandates regular internal and external penetration testing, while frameworks such as ISO 27001, SOC 2, and RBI guidelines require periodic vulnerability assessments and penetration testing to maintain regulatory compliance.
Yes. Cloud providers only secure the underlying hardware. You are responsible for protecting your applications, data, user access, and cloud configurations—making penetration testing essential to catch security gaps.
To provide an accurate scope and quotation, we require details such as the number of IP addresses for network testing, the number of dynamic pages/roles for web application testing, or the API endpoint count.
VAPT may identify indicators of zero-day and unknown vulnerabilities through manual testing, behavioral analysis, and security testing techniques, but it cannot guarantee detection of every previously unknown vulnerability.
