Latest Posts
What is vulnerability management
September 30, 2026
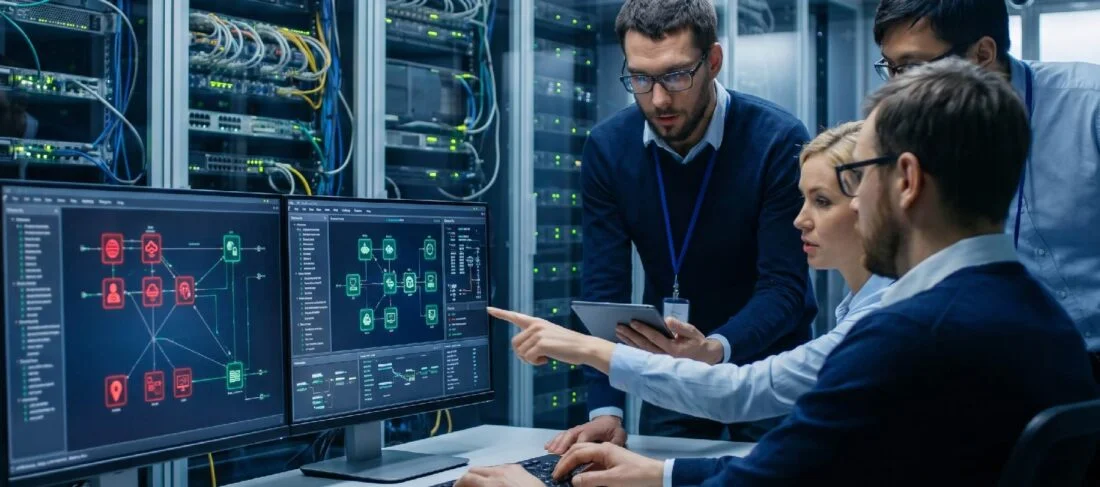
In an era where contemporary attack surfaces are constantly expanding across cloud environments, endpoints, and hybrid infrastructures, organizations face thousands of potential exploits daily. Relying on periodic health checks or basic security scans is no longer sufficient to stop sophisticated threat actors.
To maintain a robust security posture, modern enterprises must adopt Vulnerability Management—a continuous, proactive discipline designed to find, evaluate, prioritize, and fix security weaknesses before attackers can exploit them.
About Vulnerability Management
Vulnerability Management is the continuous process of identifying, classifying, prioritizing, remediating, and mitigating software vulnerabilities, misconfigurations, and system flaws across an organization’s IT infrastructure.
Rather than treating security as a one-time audit, an effective program operates as a recurring lifecycle to ensure ongoing visibility and threat prevention.
Vulnerability Assessment vs. Vulnerability Management: What’s the Difference?
A common area of confusion in cybersecurity operations is mistaking Vulnerability Scanning or Assessment for full Vulnerability Management.
 Vulnerability Assessment
A point-in-time, evaluative check. It scans networks or applications and produces a list of known security gaps.
-
Vulnerability Management
The overarching, continuous program that takes those assessment findings, prioritizes them based on real-world business risk, automates remediation, and verifies that the fixes successfully neutralized the threat.
Dimension | Vulnerability Assessment | Vulnerability Management |
Scope | Point-in-time discovery of security flaws | Continuous operational lifecycle |
Focus | Identifying known vulnerabilities | Contextual risk prioritization and threat resolution |
Outcome | Raw security reports and lists of CVEs | Measurable risk reduction, patch verification, and governance |
Execution | Automated tools running periodic scans | Integrated strategy combining tooling, human expertise, and automation |
The 5 Key Stages of the Vulnerability Management Lifecycle
To build a continuous risk-reduction model, cybersecurity teams execute a structured multi-step lifecycle:
-
 1.1. Asset Discovery & Vulnerability Identification
Continuously scan endpoints, cloud workloads, and networks using automated tools and agents to maintain a real-time inventory of digital assets and unpatched security gaps.
-
2.2. Risk Evaluation & Contextual Prioritization
Analyze detected vulnerabilities using CVSS scores and threat intelligence to prioritize critical, exploitable risks over low-priority noise.
-
3.3. Remediation & Response
Patch systems, reconfigure settings, or apply Automated Vulnerability Remediation to rapidly fix high-risk CVEs and reduce Mean Time to Remediate (MTTR).
-
4.4. Verification & Rescanning
Run automated follow-up scans to confirm that patches were successfully applied, misconfigurations are resolved, and systems remain stable.
-
5.5. Reporting, Analytics & Compliance
Generate analytics and executive reports tracking MTTR and risk reduction to demonstrate compliance with standards like ISO 27001, SOC 2, and PCI-DSS.
How StrongBox IT Elevates Your Security Posture
Implementing a comprehensive vulnerability management strategy requires combining advanced scanning engines, contextual threat intelligence, and skilled cybersecurity engineers.
StrongBox IT delivers end-to-end Vulnerability Assessment and Penetration Testing (VAPT) and Managed Vulnerability Management solutions tailored to enterprise environments:
-
 In-Depth Vulnerability Assessment & VAPT
:
StrongBox IT combines automated discovery engines with expert manual penetration testing to expose deep-seated architectural logic flaws, zero-days, and misconfigurations that traditional automated scanners miss.
-
Continuous Risk Prioritization
:
Instead of handing over hundreds of pages of raw scan logs, we prioritise vulnerabilities based on your specific business context, asset criticality, and active exploit threat intelligence.
-
Actionable Remediation Guidance
:
Our cybersecurity experts work alongside your internal teams to deliver step-by-step remediation roadmaps and re-testing verification, ensuring every critical vulnerability is remediated effectively without disrupting operational uptime.
Conclusion
Vulnerability management isn't a one-off task—it is a continuous security program essential to modern threat defense. By combining automated discovery, intelligent risk prioritization, and automated remediation workflows, organizations can reduce their attack surface and stay ahead of emerging threats.
Ready to secure your digital infrastructure? Connect with StrongBox IT to assess, manage, and remediate vulnerabilities across your enterprise.