Latest Posts
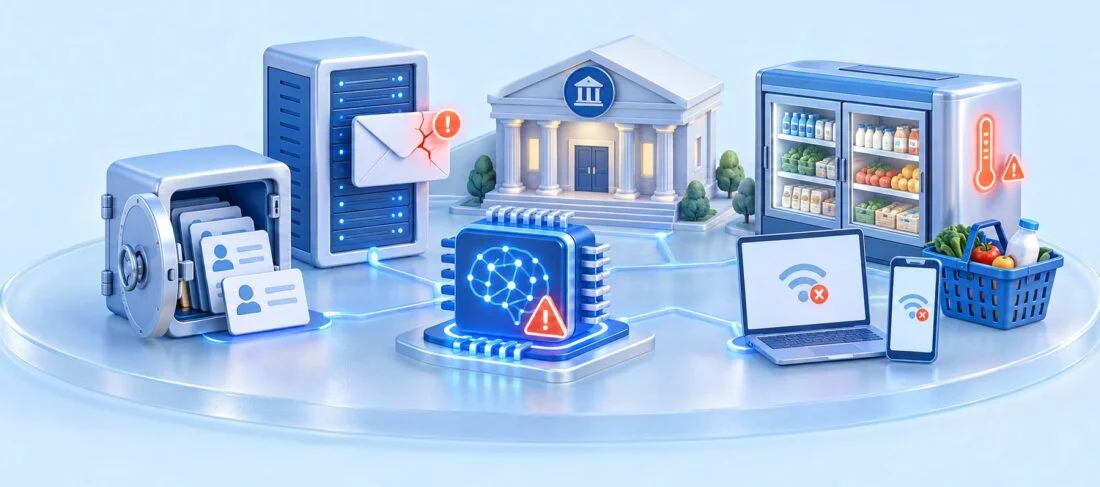
This Week in Cybersecurity: FBI Breach, AI Attacks & Critical Vulnerabilities
October 16, 2026
1. FBI Data Breach Allegedly Exposes Sensitive Employee Information
The cybercriminal group ShinyHunters claims to have breached the FBI’s recruitment portal, FBIJobs.gov, and stolen sensitive information belonging to current and former employees and job applicants. The group alleges that it obtained 2–3TB of data, although the full scale of the breach remains unverified.
The FBI has confirmed an investigation into the alleged unauthorised activity.
According to Reuters, ShinyHunters shared a sample containing information on approximately 5,000 individuals, including names, home addresses, Social Security numbers, job assignments, and some family members’ details. Parts of the sample were verified against other records, but its exact source could not be established.
The group reportedly targeted the FBI in retaliation for an advisory describing its cybercriminal activities. It demanded that the bureau correct or remove the statements, claiming they contained false allegations. The FBI’s recruitment website and applicant portal also experienced disruptions following the incident.
The origin and full extent of the alleged breach remain under investigation.
The incident highlights the risks of exposing sensitive personnel information, which could be used for phishing, harassment, identity theft, or targeted attacks. It also reinforces the need to secure recruitment platforms, assess third-party systems, and protect confidential employee records.
2. Anthropic Warns AI Agents Can Automate Cyberattacks
Anthropic warned that AI agents can automate multiple stages of cyberattacks, from identifying targets and stealing credentials to accessing networks and extracting data.
Its September 2026 threat report described campaigns involving AI models used by suspected state-backed groups, cybercriminals, and hacktivists.
These capabilities lower the technical barriers to cybercrime, allowing attackers to conduct operations faster and target more organisations with fewer resources.
3. AI-Driven Cyberattacks Hit 16 South Korean Financial Firms
South Korean regulators reported suspected AI-driven cyberattacks affecting 16 financial firms, exposing approximately 100,000 records containing personal information.
The exposed information included names, contact details, and resident registration numbers. Authorities reported no evidence that bank account or payment card numbers were compromised.
The Financial Services Commission is investigating the attacks and reviewing security practices across the financial sector. Identified gaps included missing security patches, inadequate monitoring, and weak access controls.
4. Cisco Warns of Actively Exploited Email Gateway Vulnerability
Cisco warned of an actively exploited vulnerability, tracked as CVE-2026-76519, affecting its Secure Email Gateway products. The flaw carries a CVSS score of 9.8.
Attackers can reportedly exploit malicious email attachments to gain unauthenticated root-level access to vulnerable systems. The flaw affects the Advanced Malware Protection functionality in Cisco AsyncOS.
Cisco recommends upgrading affected systems to patched software versions. The U.S. Cybersecurity and Infrastructure Security Agency added the vulnerability to its Known Exploited Vulnerabilities catalogue.
5. Cyberattack Overheats Refrigerators at French Supermarkets
Hackers remotely raised refrigerator temperatures to 50°C at French supermarkets, affecting Intermarche and Cooperative U stores.
The incident caused food losses and reported fires, prompting French authorities to launch an investigation into the attack.
Investigators identified outdated firmware in affected refrigeration systems as a concern, highlighting the risks of poorly secured, internet-connected equipment.
6. GIANT Grocery Stores Take Website and App Offline After Cyberattack
GIANT grocery stores took their website and mobile app offline after their parent company, Ahold Delhaize, reported a cybersecurity incident affecting its network.
The disruption also affected online services for Stop & Shop and Hannaford. Physical stores remained open, and officials said unfulfilled online orders would be refunded.
Ahold Delhaize took systems offline as a precaution and began restoring services. The company reported no evidence that customer, employee, or partner data had been stolen.