Latest Posts
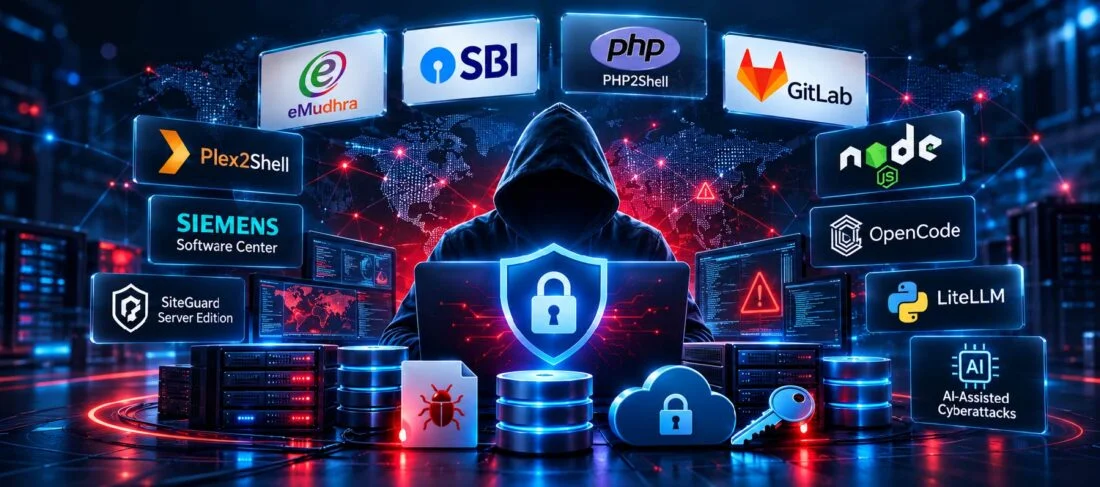
This Week in Cybersecurity: 11 Critical Threats and Developments
October 23, 2026
11 critical developments. One clear message: no organisation can afford to ignore its attack surface.
From compromised certificate authorities and customer data exposure to critical software vulnerabilities, malicious packages, and actively exploited systems, recent incidents highlight how quickly a security weakness can become a business crisis.
Here are the developments every CISO, CTO, IT administrator, and security team should be tracking.
1. eMudhra: Private Keys as Weak as “4”
Eight intermediate certificate authority keys linked to eMudhra were reportedly found to have insufficient cryptographic randomness. One reportedly corresponded to the numerical value “4.” eMudhra stated that only one of the eight keys was used and that none issued end-user certificates.
The takeaway: Weak cryptographic key generation can undermine trust in digital certificates and create risks across the wider certificate ecosystem.
2. SBI: Customer Data Found on the Dark Web
Reports identified 3,897 SBI customer records containing personal information and loan-related details within a larger dataset reportedly circulating on the dark web.
The takeaway: Exposed financial and personal information can increase the risk of fraud, targeted phishing, and identity theft, even when banking credentials are not confirmed to be compromised.
3. PHP2Shell: Critical Unauthenticated Remote Code Execution
Two critical PHP vulnerabilities, CVE-2026-109618 and CVE-2026-109619, have been reported as potential remote-code-execution risks in affected configurations. Applications built using PHP, including WordPress, Drupal, and Laravel, should be assessed against the relevant vendor advisories.
The takeaway: Unauthenticated remote code execution can allow attackers to run commands without valid credentials, potentially compromising applications and underlying servers.
4. GitLab: Critical Remote Code Execution Risk
Critical vulnerabilities affecting GitLab Community Edition and Enterprise Edition have raised concerns about remote code execution and potential server compromise. The level of exposure depends on the specific vulnerability and the version deployed.
The takeaway: Vulnerabilities in development platforms can put source code, software delivery pipelines, and sensitive development resources at risk.
5. Node.js: Critical Security Fixes
The October 2026 Node.js security release reportedly addressed multiple vulnerabilities, including a Brotli decoder flaw identified as CVE-2026-111497 and issues involving TLS certificate validation and DNS handling.
The takeaway: Vulnerabilities in runtime environments and core libraries can affect numerous applications that depend on them, making timely updates essential.
6. OpenCode: AI Provider Credentials and Unauthorised Usage
Reports of a security incident involving OpenCode raised concerns about exposed AI provider credentials and unauthorised usage. Compromised developer tools can expose API keys across multiple AI services and lead to unexpected usage and costs.
The takeaway: AI development tools can become a route to sensitive credentials, connected services, and business resources if access is not properly controlled.
7. LiteLLM: Malicious PyPI Release
LiteLLM version v1.107.0 was reported to contain malicious code capable of stealing credentials and establishing unauthorised access. The incident highlights the risks associated with compromised software release pipelines and package distribution channels.
The takeaway: A compromised software dependency can expose credentials and systems across every environment where the malicious package is installed or executed.
8. Plex2Shell: Active Exploitation
Attackers are reportedly exploiting a chain of Plex Media Server vulnerabilities, with payloads including cryptominers and proxy malware. Relevant vulnerabilities have been added to CISA's Known Exploited Vulnerabilities catalogue.
The takeaway: Internet-exposed services can become entry points for malware deployment, unauthorised access, and persistent activity when known vulnerabilities remain unpatched.
9. Siemens Software Center: Malicious DLL Loading
CVE-2026-110936 has been reported as actively exploited. The attack technique involves abusing legitimate software to load malicious dynamic-link library (DLL) files.
The takeaway: Attackers can misuse trusted applications to execute malicious code, making suspicious process behaviour and unexpected DLL loading important detection signals.
10. SiteGuard Server Edition: OS Command Injection
CVE-2026-106931 has been reported as exploited in the wild and added to CISA's Known Exploited Vulnerabilities catalogue.
The takeaway: OS command injection can allow attackers to execute unauthorised commands on vulnerable systems, potentially leading to further compromise.
11. AI-Assisted Cyberattacks: An Emerging Operational Risk
AI is increasingly relevant to both cyber defence and offensive operations. AI-assisted reconnaissance, automated attack workflows, and poorly controlled AI agents can increase the speed and scale of security incidents.
The takeaway: AI can accelerate attack activity, while agents with excessive permissions may introduce additional risks if their actions, credentials, and access are not adequately controlled.
WHAT SHOULD ORGANISATIONS DO RIGHT NOW?
- Patch with urgency: Prioritise internet-facing systems and vulnerabilities with confirmed exploitation or critical impact. Follow official vendor advisories to identify affected versions and fixes.
- Rotate exposed credentials: Include cloud keys, API tokens, database passwords, CI/CD secrets, and service-account credentials. Revoke compromised credentials before issuing replacements.
- Investigate potential compromise: Patching alone may not remove an attacker who has already established persistence or stolen credentials. Review logs, endpoints, accounts, and network activity.
- Secure the software supply chain: Validate package provenance, lock dependencies, verify container images, and protect build and release pipelines against unauthorised changes.
- Strengthen monitoring: Detect suspicious authentication, unexpected processes, unauthorised configuration changes, unusual outbound traffic, and abnormal API consumption.
- Review trust boundaries: Certificate authorities, developer tools, AI agents, security appliances, and third-party platforms can all become entry points. Apply least-privilege access and verify third-party security controls.
- Test your defences: Combine vulnerability assessments, penetration testing, secure configuration reviews, continuous monitoring, and incident-response exercises to identify gaps before attackers exploit them.
The Bigger Picture
These are distinct incidents and vulnerabilities, not evidence of one coordinated attack. However, they demonstrate a common pattern: weaknesses in trusted infrastructure, software dependencies, credential management, and access controls can have consequences far beyond the original system.
Cybersecurity is not simply about deploying tools or achieving compliance. It is about understanding where systems are exposed, reducing risks before attackers exploit them, and detecting and containing incidents quickly. Organisations that combine proactive security testing, timely remediation, and continuous monitoring are better positioned to reduce their exposure and respond effectively to threats.