Latest Posts
What is application security testing?
December 20, 2021
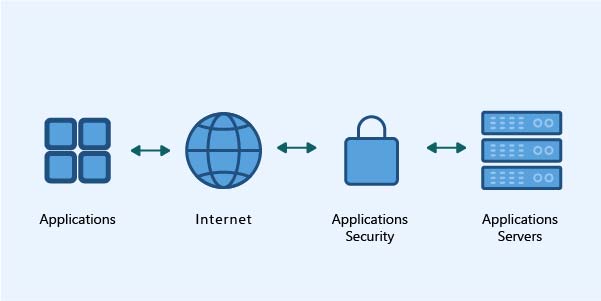
Application security testing is the process of detecting, repairing, and improving security practices to protect applications from threats throughout their entire lifecycle. Application security can assist organizations in defending all types of applications such as legacy, desktop, web, mobile.
Application security can be broadly classified into two
- SAS( Static Application Security)
- DAS( Dynamic Application Security)
Static Application Security Testing:
Static application security testing (SAST), also known as static analysis, is a methodology that analyses source code. It identifies security flaws that make applications vulnerable to attack. SAST inspects an application before the compilation. It's also referred to as white box testing. The advantages and disadvantages of Static Application Security Testing (SAST) are listed below.
ADVANTAGES OF SAST
- Fixing vulnerabilities is less expensive because it occurs at the beginning of the process.
- Provides real-time feedback as well as graphical representations of the hindrances discovered.
- SAST helps identify the precise location of the faulty code and the vulnerabilities.
- Customized reports that can be exported and tracked using readily accessible dashboards.
DISADVANTAGES OF SAST
- Needs to derive data from testing code, resulting in false positives.
- Poor at comprehending libraries or frameworks, such as API or REST endpoints.
- It is not possible to check calls for most argument values.
- Language dependence(Such as java based, python based) makes it harder to create and maintain tools, because it necessitates a separate tool for each language.
Dynamic Application Security Testing:
DAST simulates controlled attacks on a web application or service to detect security flaws in a running environment. It evaluates items during operation and provides feedback on compliance and general security issues. DAST is also referred to as "black-box" tools. These tools are utilized in the SDLC testing and quality assurance phases.
ADVANTAGES OF DAST
- Focuses on what's exploitable and covers all components to provide a holistic perspective of application security (server, custom code, open-source, services)
- It can be incorporated into the development, quality assurance, and production to provide a continuous, holistic perspective.
- The dynamic analysis allows for a more comprehensive approach to managing portfolio risk (thousands of apps) and can even scan legacy apps as part of risk management.
- Functional app testing, unlike SAST, is not language bound, allowing for the detection of runtime and environment-related errors.
DISADVANTAGES OF DAST
- It doesn't assess code or reveal weaknesses in code; instead, it focuses on issues that arise as a result of the code.
- After development is complete, it is used to remedy vulnerabilities, which is more expensive.
- Large projects necessitate technical infrastructure and several instances of the program running simultaneously.
- It generates a lot of false positives.